Compliance Control Automation Versus Manual Evidence Collection in GRC Platforms
Most GRC platforms automate workflows but leave evidence collection manual.
Adaeze Okonkwo
Automated access reviews replace yearly spreadsheets with continuous enforcement.
Most GRC platforms automate workflows but leave evidence collection manual.
Most MSP stacks connect identity tools but fail to automate complete user lifecycle workflows.
Most vendors show one screen while keeping data fragmented across separate systems underneath.
Continuous monitoring catches configuration gaps before attackers can exploit them.
Most MDR vendors stop at containment, leaving SMBs to handle recovery alone.
Duplicate and out-of-order webhooks can silently undermine security workflows.
Missed field mappings between tools silently break detection rules across your entire stack.
Syncing ticket status back to security tools prevents stale alerts from cluttering your console.
Which RMM API actually supports production integrations.
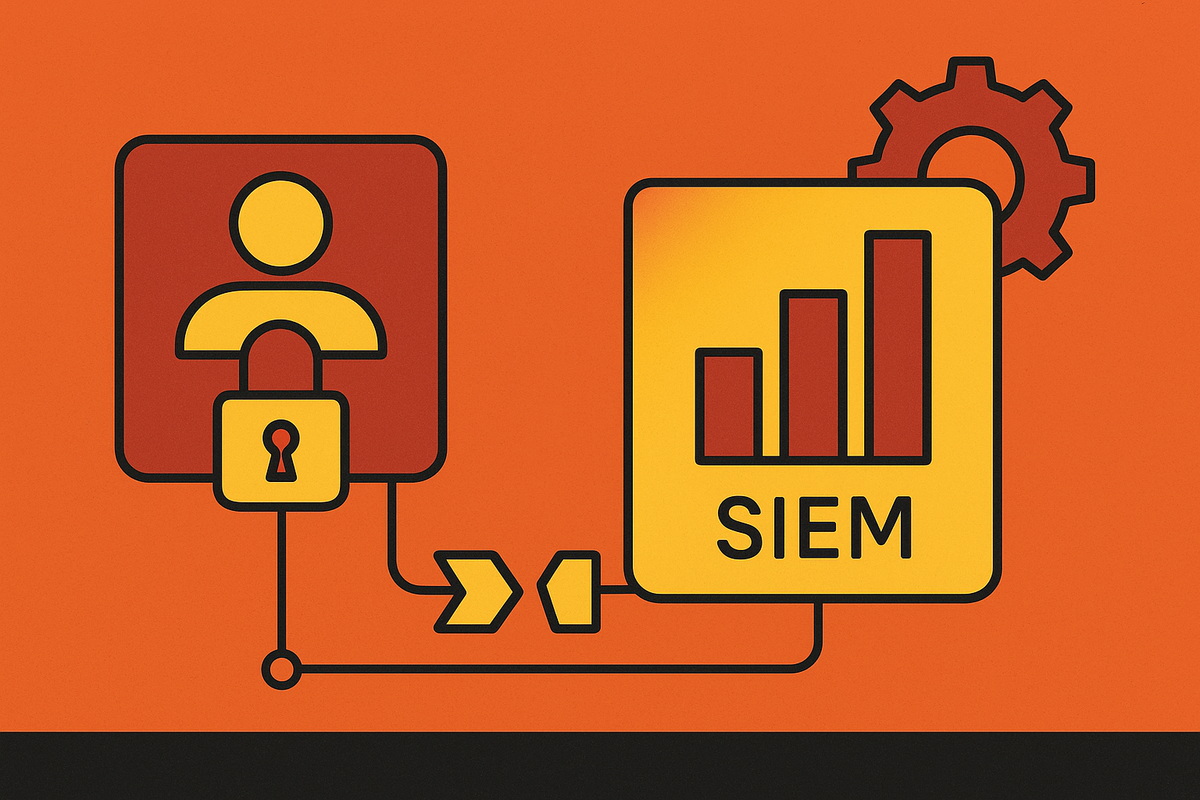
Mid-market MSPs miss cross-platform attacks because IAM and SIEM operate in separate blind spots.
Silent data pipeline failures leave your security stack blind while dashboards stay green.