Enforcement-First Architecture Versus Detect-and-Report Tool Design in SMB Security Platforms
Enforcement-first tools protect SMBs while their staff sleeps.
Security platforms for small and mid-sized businesses should be judged on whether they stop threats before execution. Enforcement-first architecture fits teams without dedicated security staff because routine protection does not wait for someone to open a dashboard. For a two-week deployment security program, the buying test is whether installed tools enforce protection across devices, identity, and configuration.
Why SMBs are structurally different from enterprises when it comes to acting on security alerts
An alert fires at 2 a.m. on a Saturday, and nobody qualified is watching. The founder is asleep. The IT generalist has no round-the-clock rotation, and the operations lead has no response playbook. The tool has detected a threat, but the attacker can still have hours or days of uncontested access. This is the failure condition that alert-based security leaves unresolved.
Responding requires more than receiving a notification. Someone needs the expertise to judge whether it is credible, the authority to contain the threat, and the availability to act immediately. Most SMBs cannot supply all three reliably, while growing volumes of weak signals make the task harder even for trained teams. Working harder cannot make up for having no staff on duty overnight. The architecture has to protect the business when its people are unavailable.
What enforcement-first architecture actually means and how it differs from detect-and-report design
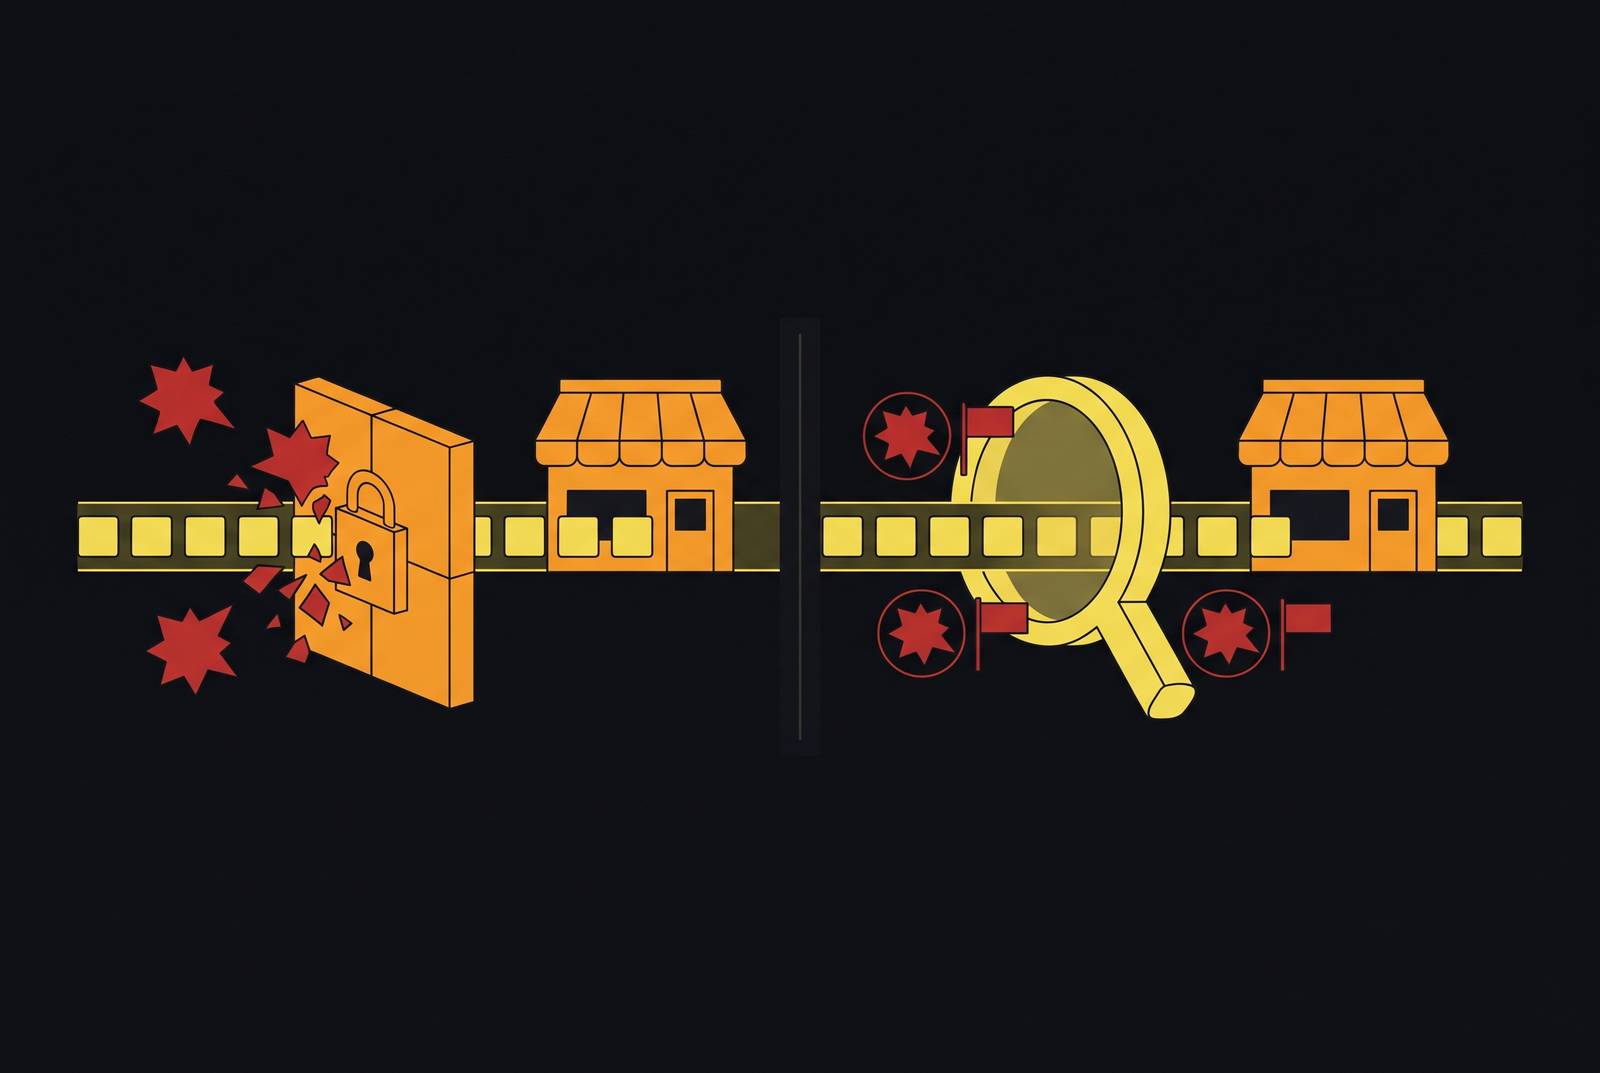
Enforcement-first design intervenes before a threat can execute. It blocks malicious techniques, unauthorized software, and exploit delivery before code runs, even while an attack is being set up in memory. Detect-and-report design instead observes suspicious code at runtime, records its behavior, and generates an alert or triggers a containment playbook. One approach aims to prevent compromise, while the other identifies an active breach so a human or automated responder can contain it.
That timing changes both the attacker’s opportunity and the defender’s workload. A threat stopped at entry has no opportunity to operate inside the business through that blocked path. A threat detected after launch has a window of access whose length depends on response speed. Automatic blocking also keeps routine threats out of the triage queue, while detection calls for ongoing checks of activity and alerts. Each approach can fail in its own way, by blocking legitimate new software or letting malware execute before the affected device is isolated.
Fileless attacks make this distinction especially important. They can use scripts and memory independently of a conventional malicious file. Once an attacker establishes a presence in memory or runs scripts to explore the environment, the scope of incident response expands sharply. Detection and response can still limit the damage, but they are now racing an attack already underway.
Why ransomware targeting of SMBs makes the enforcement gap a business-continuity question, not just a security one
For a business choosing a security platform, ransomware belongs in the buying case because an interruption can threaten the company itself. Attackers scan for remote-access tools that are exposed, software that is out of date, and credentials that have leaked. Any unprotected SMB can enter that pool. A small company’s limited visibility is not a defense against opportunistic scanning.
Verizon’s 2026 DBIR shows that small and medium-sized businesses make up the vast majority of ransomware victims, with ransomware appearing in the overwhelming majority of their breaches. Recovery costs for mid-sized companies can run into the hundreds of thousands of dollars before any ransom is paid. A meaningful share of SMBs hit by cyberattacks close or file for bankruptcy. The consequence is not simply a difficult week for IT.
Backup integrity changes the recovery picture as well. When backups are compromised, median recovery costs are many times higher than when the backups are still intact. Endpoint enforcement therefore does not replace backup protection, and backups do not replace controls that stop an attack from starting. Attackers often get in through stolen credentials and unpatched edge devices. Those are precisely the access and configuration gaps that enforcement-first architecture is designed to close before detection and triage become necessary.
How detect-and-report tools quietly depend on a response capability most SMBs do not have
Detect-and-report tools have a hidden operational dependency. Their protection model assumes that someone can turn a finding into a timely containment action. An SMB may buy the tool without paying for or building a team that can respond, yet the dashboard can still look busy and complete. Presenting that visibility as protection is misleading when the action needed to reduce risk remains outside the product and beyond the buyer’s capacity.
The missing work is specific. A qualified person must assess the signal, follow an approved response playbook, and have the authority and tools to contain the threat. Without that chain, the interval between detection and containment becomes additional dwell time, during which an attacker can move laterally, steal data, or encrypt files. A part-time IT person does not turn an alerting architecture into an enforcing one. Even a small alert queue can exceed the capacity of a business with no dedicated analyst.
The strongest answer from a buyer is that endpoint detection and response, or EDR, already includes automated response and therefore does not need a human for every incident. That is a real improvement over unattended alerts. However, automated containment still begins after execution has started, so it reduces dwell time while leaving the initial exposure intact. It also depends on correct configuration and maintained rules. Those are ongoing responsibilities that an SMB IT generalist may not be able to sustain.
What enforcement-first architecture looks like in practice across the SMB attack surface
At the endpoint layer, enforcement blocks malicious techniques, unauthorized binaries, and exploit delivery before they can launch. Application control lets software execute only if it is cryptographically verified and approved. Technique-based protections can also block methods such as heap spraying, return-oriented programming chains, and process hollowing even when there is no known vulnerability identifier. These controls target how an attack works. Apple’s Endpoint Security C API shows how this works on macOS, where a system extension can intercept process execution calls and deny authorization before a binary runs, with no need to run code in kernel space.
Ransomware protections can detect unauthorized mass encryption in real time, terminate the malicious process, and revert modified files. That is active intervention, but it is not pre-execution prevention.
At the identity layer, MFA is the baseline. It blocks the overwhelming majority of automated credential attacks and is often already included in productivity suites at no additional cost. However, strong passwords, MFA, and access reviews do not cover every attack against identity infrastructure. Identity Threat Detection and Response can use AI-driven, real-time risk evaluation to act on anomalous logins, credential misuse, and permission changes. For it to enforce protection, it must stop or contain the threat as well as report unusual behavior.
At the configuration layer, automation keeps approved settings in place, deploys updates, and corrects drift. Device controls, web filtering, and download reputation services close off more ways for attackers to get in. Coverage is part of the control itself. A device not enrolled in mobile device management is outside the reach of the enforcement architecture, regardless of how good the written policy looks.
How integrated platforms apply enforcement-first design more reliably than point tools assembled into a stack
These layers work best when they share signals. Attacks can span endpoints, identity, email, and cloud services, while isolated tools see only their own part of the activity. An endpoint control may block malicious execution yet miss a credential-based route that the attacker uses instead. Correlating endpoint signals with identity, email, and cloud activity allows enforcement to respond across those boundaries. Without those links, the IT generalist has to connect the separate systems by hand.
That linking work creates its own exposure. With five vendors, there are separate consoles, configurations, and alert queues to keep up with, and no dedicated security team to sort out the differences. An integrated platform can reduce those handoffs and make response actions more consistent. For a lean team, consistency is more useful than a standout capability that depends on expert attention elsewhere in the stack.
A new device without its security agent is an uncovered endpoint, while an agent that stops working can quietly reopen the same gap. Integrated platforms can check agent health automatically and keep coverage consistent, so staff do not have to check each vendor’s tools by hand. Continuous verification and remediation also keep configuration policy tied to running controls. None of this requires giving up visibility, because a prevention-first platform can retain rich telemetry and response capabilities while reducing unnecessary alerts.
Where the strongest objection to enforcement-first design comes from and why it does not apply the same way to SMBs
Pre-execution blocking can stop legitimate work. Novel proprietary software may trigger a false positive, and an enterprise with extensive custom tooling has a serious reason to avoid automatic disruption. This is a legitimate basis for the historical preference among enterprise security architects for layered detection models. An organization with enough analysts can take on more investigation in return for fewer automatic blocks. The objection is not wrong.
The tradeoff changes in a typical SMB environment. Most SMBs use a narrower, more stable set of commercial software, including Microsoft 365, cloud productivity tools, and industry-specific SaaS. Their exposure to false positives on novel proprietary applications is therefore substantially lower. Pre-configured enforcement policy tuned for common SMB software spares each business the work of building and maintaining its own allowlists. A platform must still handle legitimate exceptions.
Neither prevention nor detection is sufficient alone. Buyers need an approach that can do the routine protective work with the staff they have. For an enterprise, analyst capacity can absorb the cost of a detection-heavy design, while an SMB may be unable to contain lateral movement or notice a breach for days or weeks. The outcomes are sharply unequal. An SMB that gets a false positive can open a ticket, while an SMB that gets ransomware may not reopen at all.
How do you evaluate an SMB security platform before buying?
For buyers, the practical next step is to turn these distinctions into vendor questions. Ask when the platform intervenes, whether before execution, during execution, or afterward. Require an explanation of a concrete mechanism. Then ask what happens when nobody watches the dashboard for an extended period. Does protection continue automatically, or does the system accumulate alerts for someone to investigate later?
Ask whether endpoint, identity, and configuration controls work from one console or need separate tools to be linked together. Ask how new devices get protection during onboarding. If an agent loses coverage, does the platform only issue an alert, restore the control automatically, or do neither? Include continuous compliance verification in that conversation, because checking and correcting drift is different from producing a periodic audit report. Treat MFA and identity enforcement as baseline requirements.
For a two-week deployment security program, require the vendor to explain how those controls will become operational within that window. Deployment speed is a security criterion. A platform that takes months to configure leaves the enforcement gap open while that work goes on, and installing it does not by itself prove that coverage is in place. The notes supporting this comparison do not establish a verified two-week vendor shortlist or day-by-day schedule. A buying decision should therefore rest on the proposed deployment and enforced controls.
Also ask how standard deployment addresses centralized EDR and phishing-resistant MFA, which cyber insurance carriers increasingly require. Skip SIEM/SOAR platforms as the starting point when there is no dedicated staff to operate them. Favor integrated monitoring backed by automatic enforcement across device management, endpoint security, identity protection, and compliance. That combination helps a team keep its security program running when it has no staff devoted to security.